Cybersecurity governance backed by real engineering depth.
VALO Technologies helps DFW healthcarefinancial servicesprofessional servicespublic sector & SLED organizations build security programs that leadership can govern, auditors can evaluate, and technical teams can implement. We connect governance, enterprise risk, compliance, Microsoft 365 security, secure-by-design architecture, third-party risk, AI governance, and executive reporting.
From policy language to operating controls.
VALO is positioned between executive governance and technical implementation — where many security programs break down.
Cybersecurity strategy, policy and standards governance, control ownership, RACI, exception management, risk acceptance, steering cadence, awareness oversight, and executive or board reporting.
Risk assessments, risk registers, inherent and residual risk, treatment plans, risk appetite discussions, KRIs, third-party risk, and remediation tracking.
Control mapping, gap assessments, evidence management, audit readiness, security questionnaires, POA&Ms, SSP support, GRC workflows and continuous compliance.
Secure-by-design requirements translated into implementable controls across identity, networks, Microsoft 365, segmentation, firewalls, cloud connectivity, endpoint security and data protection.
What the work produces.
Concrete artifacts leadership, auditors and technical teams can use.
Security charter, policy framework, control-owner matrix, RACI, governance calendar, exception workflow and risk-acceptance process.
Enterprise risk register, risk-scoring methodology, treatment plans, third-party risk register, KRIs and prioritized remediation roadmap.
Security control matrix, framework crosswalk, maturity assessment, evidence index, gap report, POA&M, SSP support and audit-readiness tracker.
Security scorecards, KPI/KRI reporting, top-risk summaries, remediation aging, control-health trends and decision items requiring executive ownership.
Most organizations have IT. Fewer have accountable security governance.
An MSP or internal IT team can patch systems, administer Microsoft 365, configure devices and keep infrastructure running. That does not automatically create a governed security program.
A governed program defines control ownership, risk decisions, policy requirements, evidence, exceptions, third-party oversight, architecture guardrails, executive metrics and remediation accountability. VALO helps build and operate that layer while working with the technology teams already in place.
Services
Industries
GRC that understands the technology underneath the control.
VALO combines risk-management and executive governance with hands-on experience across network security, Microsoft 365 security, segmentation, firewalls, identity, endpoint controls, data protection and regulated infrastructure.
CISM, CompTIA SecurityX, PenTest+, CySA+, PCCSE and CCNP Enterprise, supported by graduate education in cybersecurity and IT management.
Healthcare, financial services, professional services, and public-sector/SLED organizations operate under regulatory, contractual, and mission requirements where weak governance becomes measurable business and operational risk.
Senior security leadership and structured GRC support for organizations that need mature governance without building a large internal security organization.
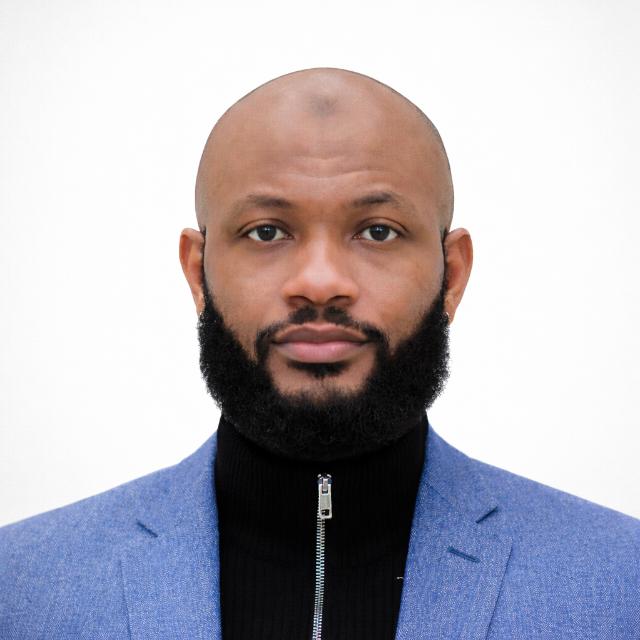
Loseini Valo Kamara
Founder & Principal Consultant
Approximately a decade of senior network security engineering across regulated environments, with graduate education in cybersecurity and IT management and certifications spanning governance, security engineering and enterprise networking.
VALO applies that background to GRC architecture: connecting business risk, policy, controls, evidence, executive reporting and the technical systems those controls depend on.
Read full bio →Methodology
Every engagement moves from risk and governance requirements into accountable implementation and sustainment.
Understand business context, regulatory exposure, architecture, controls, evidence, third parties and material risks.
Translate findings into a risk-ranked roadmap with owners, target dates, decision points and measurable outcomes.
Design governance artifacts and technical controls that your team, MSP or authorized implementation partner can execute.
Track risk, evidence, exceptions, remediation, metrics and audit readiness on an operating cadence.
Build a security program leadership can actually govern.
A 30-minute conversation to discuss your regulatory obligations, Microsoft environment, risk ownership, architecture, audit pressure, third-party exposure and the right starting point.
Schedule a conversation